How to Enable SNMP on a Raspberry Pi (snmpd Setup)

Here’s how to enable SNMP on a Raspberry Pi so your monitoring system can poll it.

1. Install snmpd

sudo apt-get update
sudo apt-get upgrade -y
sudo apt-get install snmpd -y
sudo apt-get install snmp -y

2. Edit snmpd.conf

To get it running, edit the configuration file:

sudo nano /etc/snmp/snmpd.conf

First, comment out this line so the agent doesn’t listen only on localhost:

#agentAddress  udp:127.0.0.1:161

Below the line #agentAddress udp:161,udp6:[::1]:161, add:

agentAddress udp:161

Then, below the line rocommunity public localhost, add a read-only community for your network (replace the subnet with your own):

rocommunity public 190.0.10.0/24

3. Restart the Service

sudo service snmpd restart

Related: enabling SNMP on VMware ESXi 6.5.

How to Install the Check_MK Agent on Debian Linux

Installing the Check_MK agent on Debian Linux takes just two steps. Replace %yourcheck_mk_server% with the address of your Check_MK server.

1. Install xinetd

The Check_MK agent requires xinetd:

apt-get install xinetd

2. Download and Install the Agent Package

Download the latest Check_MK agent installer from your Check_MK site and install it:

cd /tmp/
wget http://%yourcheck_mk_server%/download/check-mk-agent_***.deb
dpkg -i check*

On Red Hat or CentOS instead? See installing the Check_MK agent on Red Hat Linux.

How to Enable SNMP on VMware ESXi 6.5 with esxcli

To enable SNMP on a VMware ESXi 6.5 host, connect to it with your favorite SSH client (I use PuTTY) and run the following commands:

esxcli system snmp set --communities public
esxcli system snmp set --enable true
esxcli network firewall ruleset set --ruleset-id snmp --allowed-all true
esxcli network firewall ruleset set --ruleset-id snmp --enabled true
/etc/init.d/snmpd restart

What each step does:

  • Sets the SNMP community string (replace public with your own).
  • Enables the SNMP agent.
  • Allows all IPs through the ESXi firewall’s SNMP ruleset, then enables that ruleset.
  • Restarts the SNMP service so the changes take effect.

If you copy these commands, make sure the options begin with two hyphens (--), not a single dash. Related: enabling SNMP on a Raspberry Pi.

Exchange 2010: Where to Change Message Size Limits to Allow Larger Attachments

To allow larger attachments in Microsoft Exchange 2010, you may need to raise the message size limit in several places. A lower limit at any one of them will still block the message, so check each of these in the Exchange Management Console.

1. Organization Transport Settings

Organization Configuration > Hub Transport > Global Settings tab > Transport Settings

2. Receive Connectors

Server Configuration > Hub Transport > select a Hub Transport server > Receive Connectors > select a connector > Properties

3. Send Connectors

Organization Configuration > Hub Transport > Send Connectors > select a connector > Properties

4. Individual Mailboxes

Recipient Configuration > Mailbox > select a mailbox > Properties > Mail Flow Settings > Message Size Restrictions

5. Distribution Groups

Recipient Configuration > Distribution Group > select a group > Properties > Mail Flow Settings > Message Size Restrictions

6. Global Settings in ADSI Edit

Use ADSI Edit to connect to the Configuration container, then go to Configuration > Services > Microsoft Exchange > YourOrgName > Global Settings > Message Delivery > Properties and check these values:

  • delivContentLength
  • submissionContentLength
  • msExchRecipLimit

7. Transport Rules

Organization Configuration > Hub Transport > Transport Rules. Check for any rule that restricts attachment or message size.

Related Microsoft article: Mailbox Size Limits Are Not Enforced in a Reasonable Period of Time. See also enabling an internal SMTP relay in Exchange 2010.

How Windows DNS Scavenging Works (and What It Won’t Remove)

DNS scavenging is a Windows DNS Server feature that removes expired (stale) resource records based on their timestamps. Here are the key points to know before you rely on it.

  • Scavenging is not enabled by default. You have to turn it on.
  • It only removes dynamically updated records that have reached their timestamp age.
  • It will not remove static records, the ones you create by hand, unless you run dnscmd /AgeAllRecords. That command stamps those records with a timestamp, which makes them eligible for scavenging, so use it with care.

Viewing a Record’s Timestamp

  • Windows Server 2003: in the DNS console, open the View menu and select Advanced. Then open a record’s properties to see its timestamp.
  • Windows Server 2008 and newer: the timestamp appears as its own column in the DNS console.

Vulnerability in SSL 3.0 Could Allow Information Disclosure: Disable It with Group Policy or IE Settings

A vulnerability in SSL 3.0 could allow information disclosure. The fix is to turn off SSL 3.0 and use TLS instead. Here are two ways to do that on Windows clients: centrally with Group Policy, or per machine in Internet Explorer. To disable SSL 3.0 on the server side, see how to disable SSL 3.0 on Microsoft IIS.

Option 1: Disable SSL 3.0 with Group Policy

Use the Turn off Encryption Support setting to disable SSL 3.0 and enable TLS 1.0, TLS 1.1 and TLS 1.2 across the domain.

  1. Open Group Policy Management.
  2. Right-click the Group Policy Object to modify and select Edit.
  3. In the Group Policy Management Editor, browse to Computer Configuration > Administrative Templates > Windows Components > Internet Explorer > Internet Explorer Control Panel > Advanced Page > Turn off Encryption Support.
  4. Double-click Turn off Encryption Support and click Enabled.
  5. In the Options pane, set Secure Protocol combinations to Use TLS 1.0, TLS 1.1, and TLS 1.2.
  6. Click OK.

Option 2: Disable SSL 3.0 in Internet Explorer

To change the protocol versions Internet Explorer uses for HTTPS on a single computer:

  1. On the Internet Explorer Tools menu, click Internet Options.
  2. Click the Advanced tab.
  3. In the Security category, uncheck Use SSL 3.0 and check Use TLS 1.0, Use TLS 1.1 and Use TLS 1.2 (if available).
  4. Click OK, then exit and restart Internet Explorer.

Want to check whether a server still accepts SSLv3? Here’s a quick way to test for SSLv3.

How to Auto-Redirect a Web Page with HTML or JavaScript

There are two easy ways to send visitors from one web page to another automatically: an HTML meta refresh tag, or a few lines of JavaScript.

Redirect with an HTML Meta Refresh

This page points the browser to a different page after 2 seconds. The number in content is the delay in seconds. It’s good practice to include a manual link in case the browser doesn’t follow the redirect.

<html>
<head>
<title>A web page that points a browser to a different page after 2 seconds</title>
<meta http-equiv="refresh" content="2; URL=http://example.com/services/computing/">
<meta name="keywords" content="automatic redirection">
</head>
<body>
If your browser doesn't automatically go there within a few seconds,
you may want to go to
<a href="http://example.com/">the destination</a>
manually.
</body>
</html>

Redirect with JavaScript

You can also do it with JavaScript. This example opens the new site in a new browser window after a 4.5-second (4500 ms) delay:

<script type="text/javascript">
  window.setTimeout('window.open("http://example.com/","newsite")', 4500);
</script>

OWA Blank Page or HTTP 500 After Login? Start the Forms-Based Authentication Service

The Symptom

Outlook Web App (OWA) shows its sign-in page as normal, but after you enter your credentials it returns an HTTP 500 error or a blank page instead of opening the mailbox.

Outlook Web App sign-in page
OWA showing a blank page after login

Running IISReset /NoForce, or even rebooting the server, doesn’t change anything.

The Cause and Fix

This is typically caused by the Microsoft Exchange Forms-Based Authentication service being stopped. Open Services on the Exchange server and start it. OWA works again immediately.

Microsoft Exchange Forms-Based Authentication service stopped in Services

EqualLogic Storage Pools: Watching Volumes Load-Balance Across Members

Some new hardware arrived, which gave me a chance to experiment with EqualLogic configuration settings I wish I’d known about years earlier. The best part: watching the group automatically spread volumes across arrays.

Two Members, Different RAID, One Pool

Here I have two members, ONR1 and ONR2, each using a different RAID type:

EqualLogic group members ONR1 and ONR2 with different RAID types

Both are in the same storage pool:

EqualLogic storage pool status showing both members

And these are the volumes set up on that pool:

Volumes configured on the EqualLogic storage pool

Automatic Load Balancing

After a while, the volumes redistribute themselves across both arrays, with no manual work required:

EqualLogic volumes redistributed across both members

Pretty sweet, right? It’s one of the reasons I recommend EqualLogic. See my EqualLogic review.

How to Quickly Disable Comments on WordPress Posts and Pages

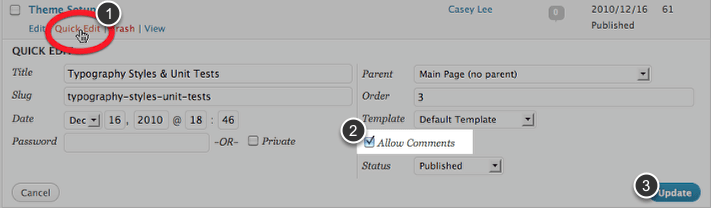
Spam comments piling up? If you have a bunch of WordPress posts or pages where you want comments turned off, Quick Edit is the fastest way to do it without opening each one.

WordPress Quick Edit link in the Posts list

Steps

  1. In the WordPress dashboard, click Posts or Pages to see the full list.
  2. Hover over an item and click Quick Edit.
  3. Check or uncheck Allow Comments.
  4. Click Update to save.

Tip: to change many at once, check several items in the list, choose Edit from the Bulk actions menu, and set Comments to “Do not allow.”