BitLocker Group Policy Settings: A Complete Example GPO

Here’s the full BitLocker Drive Encryption Group Policy I use, exported from the GPO report. It backs up TPM and BitLocker recovery information to Active Directory, uses AES 256-bit encryption, requires recovery keys to be escrowed in AD DS before encryption starts, and sets policies for operating system, fixed, and removable drives. Replace the company name and recovery folder path with your own.

Computer Configuration (Enabled)
Policies
Administrative Templates
Policy definitions (ADMX files) retrieved from the local machine.
System/Removable Storage Access
POLICY SETTING COMMENT
Removable Disks: Deny write access Disabled
System/Trusted Platform Module Services
POLICY SETTING COMMENT
Turn on TPM backup to Active Directory Domain Services Enabled
Require TPM backup to AD DS Enabled
If selected, cannot set or change TPM owner password
if backup fails (recommended default).
If not selected, can set or change TPM owner password
even if backup fails. Backup is not automatically retried.
Windows Components/BitLocker Drive Encryption
POLICY SETTING COMMENT
Choose default folder for recovery password Enabled
Configure the default folder path: \\your-domain.com\dfs\users\%USERNAME%
Specify a fully qualified path or include the computer’s environment variables in the path.
For example, enter “\serverbackupfolder”, or “%SecureDriveEnvironmentVariable%backupfolder”
Note: In all cases, the user will be able to select other folders in which to save the recovery password.
POLICY SETTING COMMENT
Choose drive encryption method and cipher strength Enabled
Select the encryption method: AES 256-bit with Diffuser
POLICY SETTING COMMENT
Choose how users can recover BitLocker-protected drives (Windows Server 2008 and Windows Vista) Enabled
Important: To prevent data loss, you must have a way to recover BitLocker encryption keys. If you do not allow both recovery options below, you must enable backup of BitLocker recovery information to AD DS. Otherwise, a policy error occurs.
Configure 48-digit recovery password: Require recovery password (default)
Configure 256-bit recovery key: Require recovery key (default)
Note: If you do not allow the recovery password and require the recovery key, users cannot enable BitLocker without saving to USB.
POLICY SETTING COMMENT
Prevent memory overwrite on restart Disabled
Provide the unique identifiers for your organization Enabled
BitLocker identification field: Your Company Name, Inc.
Allowed BitLocker identification field: Your Shorthand Company Name
POLICY SETTING COMMENT
Store BitLocker recovery information in Active Directory Domain Services(Windows Server 2008 and Windows Vista) Enabled
Require BitLocker backup to AD DS Enabled
If selected, cannot turn on BitLocker if backup fails (recommended default).
If not selected, can turn on BitLocker even if backup fails. Backup is not automatically retried.
Select BitLocker recovery information to store: Recovery passwords and key packages
A recovery password is a 48-digit number that unlocks access to a BitLocker-protected drive.
A key package contains a drive’s BitLocker encryption key secured by one or more recovery passwords
Key packages may help perform specialized recovery when the disk is damaged or corrupted.
Windows Components/BitLocker Drive Encryption/Fixed Data Drives
POLICY SETTING COMMENT
Allow access to BitLocker-protected fixed data drives from earlier versions of Windows Enabled
Do not install BitLocker To Go Reader on FAT formatted fixed drives Disabled
POLICY SETTING COMMENT
Choose how BitLocker-protected fixed drives can be recovered Enabled
Allow data recovery agent Enabled
Configure user storage of BitLocker recovery information:
Allow 48-digit recovery password
Allow 256-bit recovery key
Omit recovery options from the BitLocker setup wizard Disabled
Save BitLocker recovery information to AD DS for fixed data drives Enabled
Configure storage of BitLocker recovery information to AD DS: Backup recovery passwords and key packages
Do not enable BitLocker until recovery information is stored to AD DS for fixed data drives Enabled
POLICY SETTING COMMENT
Configure use of passwords for fixed data drives Enabled
Require password for fixed data drive Enabled
Configure password complexity for fixed data drives: Allow password complexity
Minimum password length for fixed data drive: 8
Note: You must enable the “Password must meet complexity requirements” policy setting for the password complexity setting to take effect.
POLICY SETTING COMMENT
Deny write access to fixed drives not protected by BitLocker Enabled
Windows Components/BitLocker Drive Encryption/Operating System Drives
POLICY SETTING COMMENT
Allow enhanced PINs for startup Enabled
Choose how BitLocker-protected operating system drives can be recovered Enabled
Allow data recovery agent Enabled
Configure user storage of BitLocker recovery information:
Allow 48-digit recovery password
Allow 256-bit recovery key
Omit recovery options from the BitLocker setup wizard Disabled
Save BitLocker recovery information to AD DS for operating system drives Enabled
Configure storage of BitLocker recovery information to AD DS: Store recovery passwords and key packages
Do not enable BitLocker until recovery information is stored to AD DS for operating system drives Enabled
POLICY SETTING COMMENT
Configure minimum PIN length for startup Enabled
Minimum characters: 4
POLICY SETTING COMMENT
Require additional authentication at startup Enabled
Allow BitLocker without a compatible TPM Enabled
(requires a startup key on a USB flash drive)
Settings for computers with a TPM:
Configure TPM startup: Allow TPM
Configure TPM startup PIN: Allow startup PIN with TPM
Configure TPM startup key: Allow startup key with TPM
Configure TPM startup key and PIN: Allow startup key and PIN with TPM
POLICY SETTING COMMENT
Require additional authentication at startup (Windows Server 2008 and Windows Vista) Enabled
Allow BitLocker without a compatible TPM Enabled
(requires a startup key on a USB flash drive)
Settings for computers with a TPM:
Configure TPM startup key: Allow startup key with TPM
Configure TPM startup PIN: Allow startup PIN with TPM
Important: If you require the startup key, you must not allow the startup PIN.
If you require the startup PIN, you must not allow the startup key. Otherwise, a policy error occurs.
Note: Do not allow both startup PIN and startup key options to hide the advanced page on a computer with a TPM.
Windows Components/BitLocker Drive Encryption/Removable Data Drives
POLICY SETTING COMMENT
Allow access to BitLocker-protected removable data drives from earlier versions of Windows Enabled
Do not install BitLocker To Go Reader on FAT formatted removable drives Disabled
POLICY SETTING COMMENT
Choose how BitLocker-protected removable drives can be recovered Enabled
Allow data recovery agent Enabled
Configure user storage of BitLocker recovery information:
Allow 48-digit recovery password
Allow 256-bit recovery key
Omit recovery options from the BitLocker setup wizard Disabled
Save BitLocker recovery information to AD DS for removable data drives Enabled
Configure storage of BitLocker recovery information to AD DS: Backup recovery passwords and key packages
Do not enable BitLocker until recovery information is stored to AD DS for removable data drives Enabled
POLICY SETTING COMMENT
Configure use of passwords for removable data drives Enabled
Require password for removable data drive Enabled
Configure password complexity for removable data drives: Allow password complexity
Minimum password length for removable data drive: 8
Note: You must enable the “Password must meet complexity requirements” policy setting for the password complexity setting to take effect.
POLICY SETTING COMMENT
Control use of BitLocker on removable drives Enabled
Allow users to apply BitLocker protection on removable data drives Enabled
Allow users to suspend and decrypt BitLocker protection on removable data drives Enabled
POLICY SETTING COMMENT
Deny write access to removable drives not protected by BitLocker Disabled

How to Find Which Replica Disk a VMware View Linked Clone Uses

In VMware View (Horizon), each linked clone desktop is built from a replica disk. When you need to know which linked clones depend on which replica, for example before cleaning up storage, you can find out from the ESX/ESXi console.

Steps

1. Log in to the ESX host as root. On ESXi, open the console, press Alt+F1, and type unsupported (or use SSH).

2. Find every small descriptor .vmdk that points to a replica parent:

find /vmfs/volumes/ \( -size -1500c \) -name '*.vmdk' -exec grep replica {} -H \; | grep 'parentFileNameHint=' > replicalist.txt

3. Make the output easier to read by inserting an arrow between each clone and its replica:

sed 's/:/-->>/' < replicalist.txt > replicalist2.txt

4. View the results:

less replicalist2.txt

The output looks like this:

/vmfs/volumes/4cceb02c-6fba721c-a0ff-001e0b1f4ca2/test-2/test-2.vmdk-->>parentFileNameHint="/vmfs/volumes/4cceb02c-6fba721c-a0ff-001e0b1f4ca2/replica-8581f32c-a851-448e-8ea8-/replica-8581f32c-a851-448e-8ea8-.vmdk"
/vmfs/volumes/4cceb02c-6fba721c-a0ff-001e0b1f4ca2/test-1/test-1.vmdk-->>parentFileNameHint="/vmfs/volumes/4cceb02c-6fba721c-a0ff-001e0b1f4ca2/replica-8581f32c-a851-448e-8ea8-/replica-8581f32c-a851-448e-8ea8-.vmdk"

Reading the Results

  • Linked clones are on the left of -->> and their replica is on the right. Other VMs besides pool desktops may also appear.
  • The replica name in vCenter Server is longer than the folder and .vmdk name in the datastore. For example, vCenter shows replica-ae5923a9-4991-41e7-ba03-07c61429d839 while the .vmdk is replica-ae5923a9-4991-41e7-ba03-.vmdk.

Make Windows Prefer Wired LAN over Wi-Fi with a DHCP Default Router Metric

When a laptop is connected to both wired Ethernet and Wi-Fi, you usually want traffic to go over the wired LAN. If your Windows Server 2003/2008 DHCP server hands out the wireless addresses, you can make that happen automatically by giving the wireless gateway a higher route metric. Windows always prefers the route with the lower metric.

Set the Metric on the Wireless DHCP Scope

  1. In the DHCP console, right-click Scope Options on your wireless scope and choose Configure Options.
  2. Open the Advanced tab.
  3. For Vendor class, choose Microsoft Windows 2000 Options.
  4. Check 003 Microsoft Default Router Metric Base.
  5. Enter a value that suits your network. I use 0x1f4 (500), which gives the wireless route an effective metric of 525, higher than every other network metric we use.

Optional: Set the Wired Scopes Too

You can repeat these steps on your wired scopes with a value of 0, which leaves them at the base metric of 10. This is only necessary if their current base value is higher than 10. Check it by running route print from a command prompt.

For more detail, see Microsoft’s TechNet article on DHCP options and search the page for “default router metric base”.

PPTP VPN (GRE) Broken After VMware vSphere 5.5 Upgrade? Switch the Sophos UTM VM to VMXNET3

You’d think upgrading VMware would be transparent to the guest operating system. Not with vSphere 5.5: it broke my PPTP VPN. Here’s how I fixed it.

I run a Sophos UTM 9 firewall as a VM appliance on VMware 5.5. It works great, but to get PPTP VPN (which relies on GRE) working again after the upgrade, I had to change the VM’s settings and swap its network adapters from E1000 to VMXNET3.

1. Change the Guest Operating System Type

In the VM properties, change the guest operating system from “Other Linux”:

VM guest OS set to Other Linux 64-bit

To “Red Hat Enterprise Linux 6”:

VM guest OS changed to Red Hat Enterprise Linux 6 64-bit

This lets you add virtual network adapters other than the E1000:

E1000 virtual network adapter

2. Remove the Existing NICs

VM with the existing network adapters removed

3. Re-add the NICs as VMXNET3

Adding a VMXNET 3 network adapter

When you’re done, the VM should look like this:

VM with VMXNET3 network adapters added

EqualLogic Storage Pools: Watching Volumes Load-Balance Across Members

Some new hardware arrived, which gave me a chance to experiment with EqualLogic configuration settings I wish I’d known about years earlier. The best part: watching the group automatically spread volumes across arrays.

Two Members, Different RAID, One Pool

Here I have two members, ONR1 and ONR2, each using a different RAID type:

EqualLogic group members ONR1 and ONR2 with different RAID types

Both are in the same storage pool:

EqualLogic storage pool status showing both members

And these are the volumes set up on that pool:

Volumes configured on the EqualLogic storage pool

Automatic Load Balancing

After a while, the volumes redistribute themselves across both arrays, with no manual work required:

EqualLogic volumes redistributed across both members

Pretty sweet, right? It’s one of the reasons I recommend EqualLogic. See my EqualLogic review.

How to Quickly Disable Comments on WordPress Posts and Pages

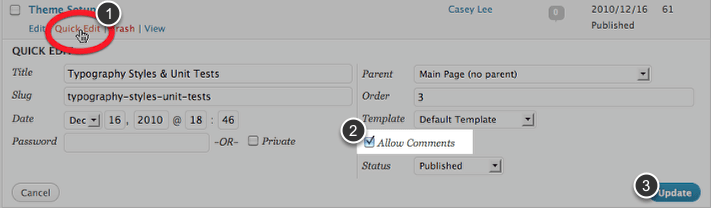
Spam comments piling up? If you have a bunch of WordPress posts or pages where you want comments turned off, Quick Edit is the fastest way to do it without opening each one.

WordPress Quick Edit link in the Posts list

Steps

  1. In the WordPress dashboard, click Posts or Pages to see the full list.
  2. Hover over an item and click Quick Edit.
  3. Check or uncheck Allow Comments.
  4. Click Update to save.

Tip: to change many at once, check several items in the list, choose Edit from the Bulk actions menu, and set Comments to “Do not allow.”

How to Configure Incoming Email in SharePoint 2010 with Exchange 2010 (Step by Step)

This guide continues setting up a SharePoint 2010 farm, focusing on configuring incoming email so messages are delivered straight into SharePoint document libraries and lists. When SharePoint 2007 was released, there was a lot of discussion and rumors around Exchange 2007 being the last version of Exchange to provide Public Folder support, and that SharePoint 2007 was going to be its alternative. Microsoft quickly changed its stance and continues to support Public folders in Exchange 2010. However, there still might be a number of compelling reasons why you would want to consider storing incoming email messages in SharePoint 2010 document libraries, instead of public folders.

In today’s post, I will provide you with a comprehensive step by step guide in configuring your SharePoint 2010 server in conjunction with Exchange 2010, to provide successful delivery of incoming email directly to your SharePoint Web Applications.

The environment

It consists of the following servers which would form a common basis in most large organizations.

  • Windows 2008 R2 server running Active Directory Domain Services
  • Windows 2008 R2 server running SQL 2008R2
  • Windows 2008 R2 server running SharePoint 2010 RTM
  • Windows 2008 R2 server running Exchange 2010 RTM
  • Windows 7 client running Office 2010 RTM

The SMTP service

SharePoint 2010 is reliant on the SMTP service which is a Windows 2008 feature and we must install this on our SharePoint 2010 front-end web server.

Navigate to your Start Menu / Administrative Tools / Server Manager. Click on the Features node and select Add Feature. Scroll down and select SMTP Server and click on Add Required Role Services.

image_thumb1

Click Next, Next and Install.

image_thumb2

Click Close

We now need to install the IIS 6.0 Management Tools on our Windows 2008 R2 server in order to configure our SMTP service. If IIS 6.0 Manager is not already installed you must do so via, Start / Administrative Tools / Server Manager. Click on the Roles node and select Role / Add Role Services. Then select Management Tools and IIS 6 Management compatibility. Click Install.

We can now launch the IIS 6 Manager via Start / Administrative Tools.

image_thumb3

Right click on SMTP Virtual Server #1 and select properties.

Under the General tab, I have enabled logging and encourage doing so at the start in the event we need to do some troubleshooting. You can turn logging off after successful testing.

image_thumb4

Click on the next tab, “Access”.

Click on “Authentication” and ensure that Anonymous access is selected.

image_thumb5

Next, click on “Connection” and ensure “All except the list below” is selected.

image_thumb6

Finally, click on “Relay”, and ensure that “Only the list below” is selected and that “Allow all computers which successfully authenticate to relay, regardless of the list above” is also checked.

image_thumb7

Now click on the Messages Tab and make any necessary adjustments that you see fit, such as potentially increasing the message size to allow for the delivery of larger emails with attachments into your SharePoint Libraries and Lists.

image_thumb8

Next click on the Delivery Tab in which I normally leave all the defaults in place.

image_thumb9

We can skip the LDAP routing tab as there are no settings required to be configured in this area.

Lastly, the Security tab should list the default permissions as per the below. No changes are necessary in this area.

image_thumb10

Next, open the “Domains” area within IIS 6 Manager and a domain name should be listed, which by default is the fully qualified domain name of the machine.

Right click on the Domain Name and select properties and take note of the Drop directory.

image_thumb11

Finally, we now just need to confirm that our SMTP service is set to start automatically in the event the server is restarted. I can tell you now that the service is by default set to Manual.

Venture into Start / Administrative Tools / Services.

Scroll down your list of services and ensure that the Simple Mail Transfer Protocol (SMTP) is set to Start-up type, Automatic.

image_thumb12

We have now completed the configuration of our SMTP service on our SharePoint Server.

Exchange 2007/2010 Connectors

Part two of the implementation of configuring incoming email in SharePoint is to configure our connectors in Microsoft Exchange. Now even though this is not a requirement, most organizations running SharePoint 2010 or 2007 will also be running a recent version of Microsoft Exchange, hopefully either 2007 or 2010. Exchange 2010 or 2007 will provide you with that extra layer of protection ensuring that all the necessary message hygiene has been performed via its inbuilt Anti Spam Agents on the Edge or Hub Transport Server in conjunction with some form of email antivirus such as Microsoft’s Forefront for Exchange, before the message is delivered to the SharePoint 2010 List or Library.

My instructions and screen captures below are from an Exchange 2010 server which are pretty much identical and applicable to Exchange 2007.

Let’s begin by launching the Exchange Management Console / Organization Configuration / Hub Transport.

Click on Send Connectors / Actions / New Send Connector.

Type in a descriptive name for your Send Connector and then select Internal as the type.

image_thumb13

Click Add and enter the Address space as the fully qualified domain name of the server where the SMTP service is installed (i.e. your SharePoint Server)

image_thumb14

Click Next

Enter the IP address of the server which also hosts the SMTP service.

image_thumb15

Click Next

Select “None” as your smart host authentication settings

image_thumb16

Click Next

Ensure your Hub Transport Server has been added.

image_thumb17

Click Next

image_thumb18

Click New and then click Finish

The end result will be that the Send connector will route email to the SMTP service sitting on our SharePoint Server.

image_thumb19

The Directory Management Service

SharePoint 2010 allows you to leverage Active Directory Domain Services (AD DS) so that contacts that are created when you email enable document libraries or lists are stored in a designated Organizational Unit within your AD DS infrastructure. So why would you want to enable Directory Management Service? Purely for the fact that by storing these contacts in AD, you are allowing your users to locate email enabled libraries and lists easily from within their Outlook Address book.

Let’s begin by creating an Organizational Unit in Active Directory.

From your Active Directory server, click Start / Administrative Tools / Active Directory Users and Computers.

Right click on your domain object and select New / Organizational Unit

Type in a descriptive name

image_thumb20

Click Ok.

The next step is imperative and very important that we get this right. I have seen on many occasions where incorrect permissions were applied and all sorts of problems were encountered when libraries or list were email enabled.

In summary, we need to provide our Central Administration Application pool identity account specific permissions to our recently created Organizational Unit to be used for creating and deleting contacts for our SharePoint 2010 libraries and lists when they are either email enabled or email disabled.

Right click on the recently created Organizational Unit and click on Delegate Control. This will invoke the Delegation of Control Wizard.

image_thumb21

Click Next.

We will now add the Central Administration application pool account which you can confirm from IIS Manager as per the below screen capture.

image_thumb22

Add the necessary Account.

image_thumb23

Click Next.

Click Create a custom task to delegate.

image_thumb24

Click Next

Click “This folder, existing objects in this folder, and creation of new objects in this folder’.

image_thumb25

Click Next

Click on Create All Child Objects and Delete All Child Objects.

image_thumb26

Click Finish.

Before we finish off our configuration of AD DS and the Directory Management Service we need to provide our Central Administration application pool account with Delete Subtree permissions.

We need to ensure that “Advanced Features” from within Active Directory Users and Computers (ADUC) is active before we venture into the security tab of our SharePoint organizational unit. If you do not enable Advanced Features, the security tab will not be visible.

From within ADUC, click on View and select Advanced Features.

Right click on our SharePoint 2010 Organizational Unit and select Properties.

Click on the Security Tab / Advanced /and Edit the CA Application Pool Identity Account.

image_thumb27

Select Allow for “Delete Subtree”

image_thumb28

Click on OK and Apply.

After assigning these permissions, you must run IISRESET on your SharePoint server.

Configuring Incoming e-mail settings in Central Administration

Navigate to Central Administration / System Settings / Configure incoming e-mail settings.

image_thumb29

Select Yes to “Enable site on this server to receive e-mail”

Select “Automatic” for Setting mode.

Select “Yes” to use the SharePoint Directory Management Service to create distributions groups and contacts.

Enter your Active Directory container details, i.e. the Organizational Unit container that we created specifically for our SharePoint 2010 contacts.

Ensure that your SMTP server details are correct, this should be the fully qualified domain name of your SMTP service that was installed on your SharePoint Server.

image_thumb30

Finally, ensure “Accept mail from all e-mail servers” is selected.

image_thumb31

Click OK.

Please note that this process will configure the necessary permissions on the email drop folder listed in IIS 6 Manager. In summary, the following permissions are added;

WSS_Admin_WPG – Full Control and

WSS_WPG – Read & Execute / List folder Contents / Read

image_thumb32

Ensure that these accounts are added successfully and on the rare occasion in which it isn’t, you will need to add them manually.

Testing the configuration

From within any document library or list, click on Library / Library Settings.

image_thumb33

Click on Incoming e-mail settings.

Select “Yes” to allow this document library to receive e-mail.

Select your email attachment options and ensure that Save original e-mail is set to Yes.

Lastly, ensure that you Accept e-mail messages from any sender is selected.

image_thumb34

Click OK.

This is your first step to ensure that all of the above configuration is in place. If you do receive an error, it’s most likely going to be permissions related against your Organizational Unit, i.e. SharePoint may not have the privilege to add the contact in Active Directory.

Let’s navigate back to ADUC and confirm that our “testing” contact is created under the SharePoint 2010 Contacts Organizational Unit.

image_thumb35

Let’s next navigate to our Exchange 2010 server and ensure it is also listed there with an SMTP address against it.

Launch your Microsoft Exchange Management console and navigate to Recipient Configuration / Mail contact.

image_thumb36

Right click on the Contact and select Properties / E-Mail Addresses.

Ensure that both an internal and external routable email address is listed.

image_thumb37

From your favorite email client, send a test email to the document libraries’ external SMTP address.

Navigate to your recently email enabled document library and hopefully after a couple of minutes (SharePoint Job timer service delay) you should have received your test email.

image_thumb38

Well! That’s all that is to it, from start to finish. Apart from sending a test email, there are a couple of other scenarios that you should test to ensure complete seamless integration with the SharePoint 2010 Directory Management Service. Within the same document library, modify the email address to something different and ensure that this change also flows through to Active Directory. You should also try disabling incoming email from that same library and ensure that the contact is completely removed from Active Directory. If you pass all of these tests scenarios, then we are comfortable in knowing that the correct delegation was provided to our Central Administration Pool Account against our SharePoint Contacts Organizational Unit.

Shrink the Windows Page File on VMs with a Group Policy Registry Preference

I run a lot of virtual machines on a tight budget with thin-provisioned storage, so wasted disk space bothers me. A large default page file on every Windows VM adds up quickly. To keep it in check, I set a fixed page file size with a registry preference in my “Server Optimization” GPO.

GPO Location

Computer Configuration
  Preferences
    Windows Settings
      Registry

Registry Item Settings

ActionUpdate
HiveHKEY_LOCAL_MACHINE
Key pathSYSTEM\CurrentControlSet\Control\Session Manager\Memory Management
Value namePagingFiles
Value typeREG_MULTI_SZ
Value datac:\pagefile.sys 1000 1000

The value data sets the page file on C: to a fixed 1,000 MB (initial and maximum size). On the Common tab, I leave all options (stop processing on error, remove when no longer applied, apply once) set to No.

Slap that in your GPO, and the change takes effect after the next Group Policy refresh and reboot.

Group Policy Security Tip: “Do Not Display Last User Name” at Logon

One Group Policy setting I always enable is Interactive logon: Do not display last user name. If the logon screen shows the last user name, you’re handing anyone at the keyboard half the credentials they need.

Where to Find the Setting

Computer Configuration
  Policies
    Windows Settings
      Security Settings
        Local Policies
          Security Options
PolicySetting
Interactive logon: Do not display last user nameEnabled

Link the GPO to the OUs containing your servers and workstations, and users will have to type both their user name and password at logon.

Fix Exchange 2010 Event ID 1020: “Provided Valid Credentials, but Is Not Authorized”

Exchange Server 2010 administrators often run into this error:

The account 'Domain\Administrator' provided valid credentials, but is not authorized to use the server; failing authentication.
Event ID: 1020

What It Means

The account is missing permissions on the receive connector. Specifically, it doesn’t have the ms-Exch-SMTP-Submit right on the Hub Transport or Edge Transport server that hosts the receive connector, even though it may be allowed to use that connector for inbound messages.

Receive connectors are assigned predefined permission groups, which grant sets of permissions to users, computers, and security groups. Those groups determine who can submit messages through the connector. In Exchange 2010 the predefined permission groups can’t be modified and you can’t create new ones, so the fix is to grant the right directly.

How to Fix It

Open the Exchange Management Shell and list your receive connectors, noting the identity of the one on the affected server:

Get-ReceiveConnector

Check the user’s current permissions on that connector:

Get-ReceiveConnector -Identity "SERVERNAME\Default SERVERNAME" | Get-ADPermission -User UsernameHere | Format-Table -View User

Grant the submit permission:

Add-ADPermission -Identity "Default SERVERNAME" -User Username -ExtendedRights ms-Exch-SMTP-Submit

If that doesn’t solve it, use the Exchange troubleshooting tools available from the Exchange Management Console to dig further.